Security Engineering: Automating SSH Brute-Force Protection with Fail2Ban
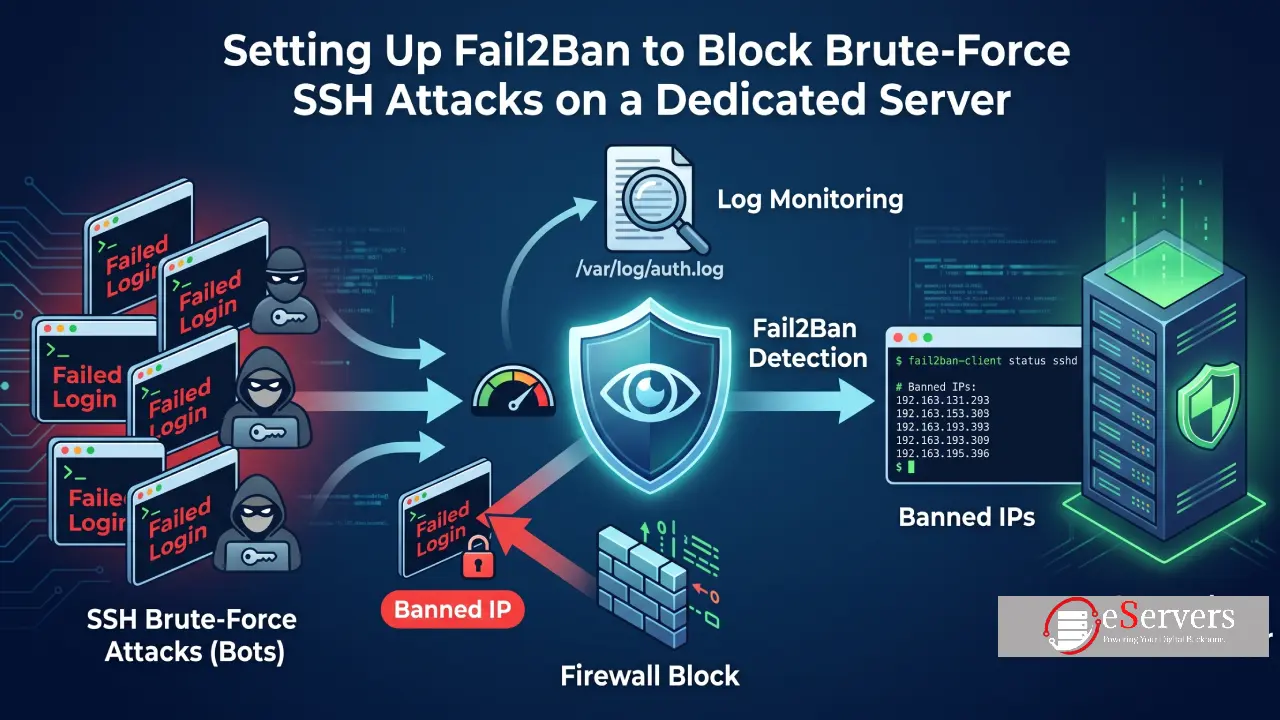
Within minutes of a Linux server receiving a public IP address, automated scanners begin attempting to brute-force the SSH daemon (port 22). While disabling password authentication in favor of SSH keys (like Ed25519) prevents unauthorized access, the daemon still consumes CPU cycles and clutters logs processing the initial cryptographic handshakes of thousands of malicious requests.
To mitigate this resource drain at the network edge, systems administrators deploy Fail2Ban. This daemon parses authentication logs (such as /var/log/auth.log or the systemd journal) for regex patterns matching failed logins. Upon reaching a defined threshold, it dynamically inserts a drop rule into the local firewall (iptables, nftables, or ufw), blocking the offending IP completely.
Here is a technical blueprint for safely deploying and configuring Fail2Ban on Ubuntu 24.04 or Debian 12.
Pre-Deployment Safety Warning
CRITICAL: Before modifying firewall behaviors, ensure you have a fallback method to access your server (e.g., out-of-band IPMI console, or a secondary SSH session kept open). A misconfigured Fail2Ban jail can permanently ban your own IP address.
Step 1: Daemon Installation
Update your package index and install Fail2Ban from the standard repositories:
sudo apt update
sudo apt install -y fail2ban
Enable the service to start on boot and launch it immediately:
Bash sudo systemctl enable --now fail2ban sudo systemctl status fail2ban Step 2: Configuration Isolation Fail2Ban’s primary configuration resides in /etc/fail2ban/jail.conf. Never modify this file directly. Upstream package updates will overwrite it, destroying your custom ruleset.
Always duplicate it to a .local file, which Fail2Ban automatically reads as an override:
Bash sudo cp /etc/fail2ban/jail.conf /etc/fail2ban/jail.local All subsequent edits should be made exclusively in jail.local.
Step 3: Jail Configuration Open /etc/fail2ban/jail.local in your preferred text editor.
- Whitelisting Trusted IPs First, locate the [DEFAULT] block. You must whitelist your administrative IP addresses (home, office, VPN) to prevent accidental lockouts:
Ini, TOML [DEFAULT] ignoreip = 127.0.0.1/8 ::1 203.0.113.50 (Separate multiple IP addresses with a space).
- Tuning the SSH Jail Next, locate the [sshd] block and configure the enforcement metrics:
Ini, TOML [sshd] enabled = true port = ssh maxretry = 5 findtime = 10m bantime = 1h What these parameters control:
maxretry: The number of failed attempts allowed before a ban is triggered.
findtime: The time window in which the failures must occur (e.g., 5 failures within 10 minutes).
bantime: The duration of the firewall block (e.g., 1h for one hour, 1d for one day, or -1 for a permanent ban).
Note: If your SSH daemon operates on a non-standard port, explicitly define it (e.g., port = 2222).
Step 4: Application and Verification Restart the service to load your overrides:
Bash sudo systemctl restart fail2ban Verify that the sshd jail is actively monitoring:
Bash sudo fail2ban-client status sudo fail2ban-client status sshd The output will display the number of currently failed attempts, the total number of banned IPs, and the specific IP addresses currently residing in the jail.
Step 5: Manual Administration If a legitimate user triggers a ban (or if you accidentally ban a test machine), you can manually remove the firewall block using the Fail2Ban client:
Bash sudo fail2ban-client set sshd unbanip <IP_ADDRESS> To flush all active bans across all configured jails simultaneously in an emergency:
Bash sudo fail2ban-client unban --all Conclusion Fail2Ban is a critical layer of automated host defense. Once SSH is secured, the exact same jail.local syntax can be extended to protect other public-facing services like Nginx, Apache, or Postfix by enabling their respective built-in jails.